FAQ
How Snare works: common questions
What are the four Snare deployment pathways?
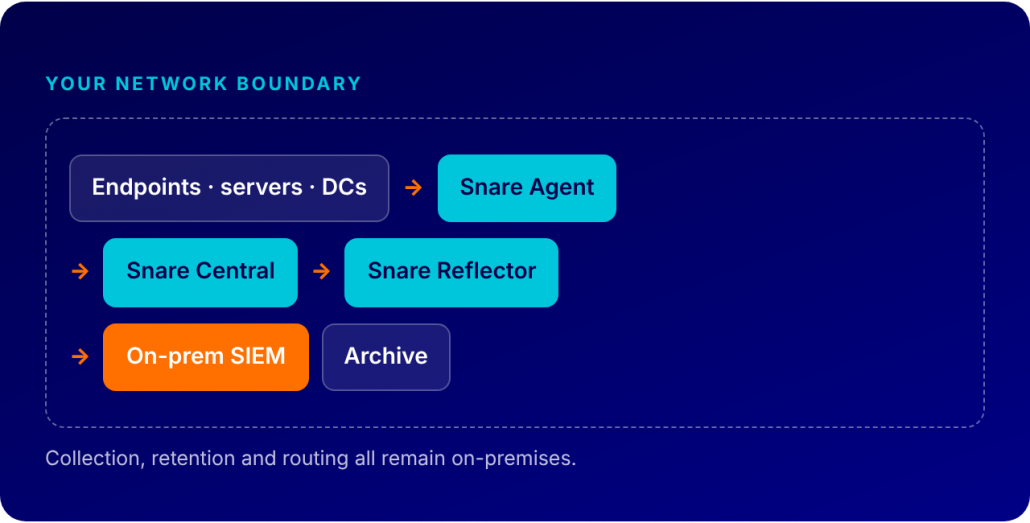
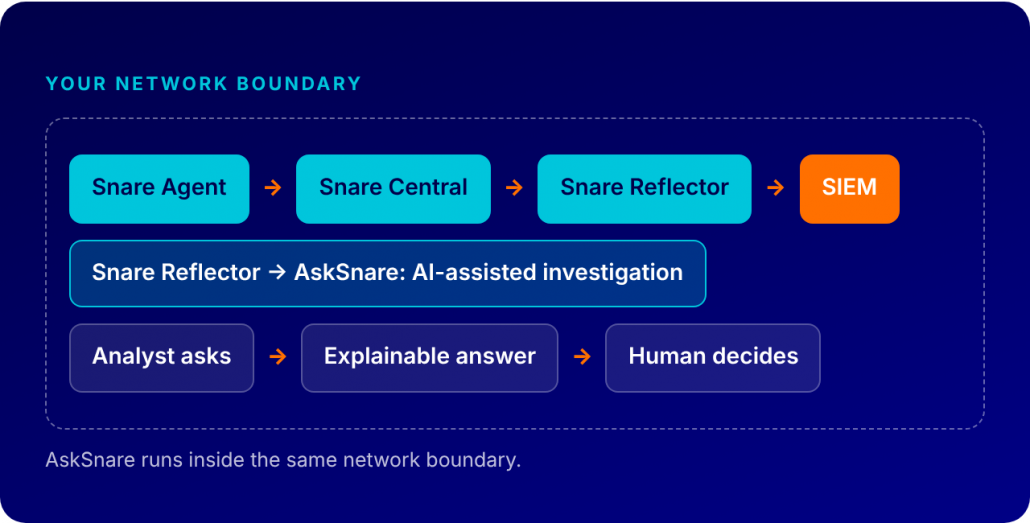
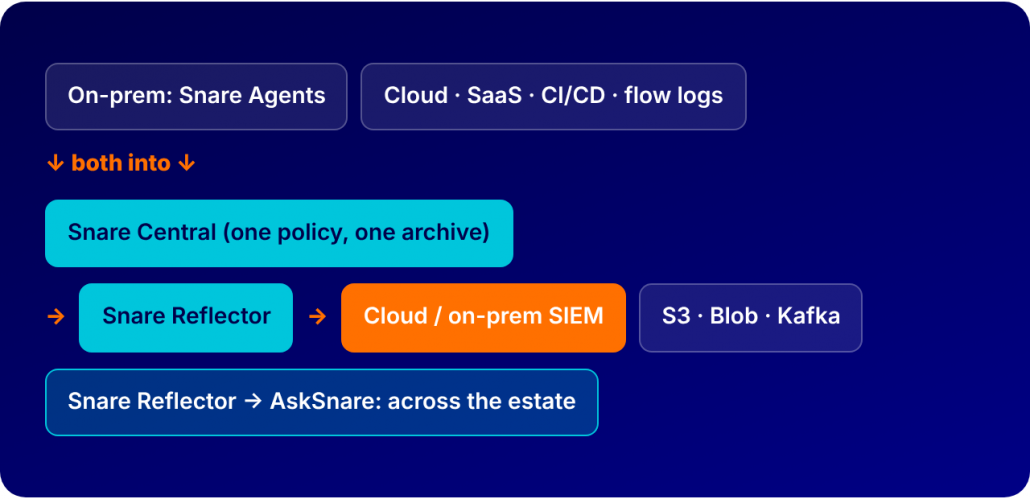
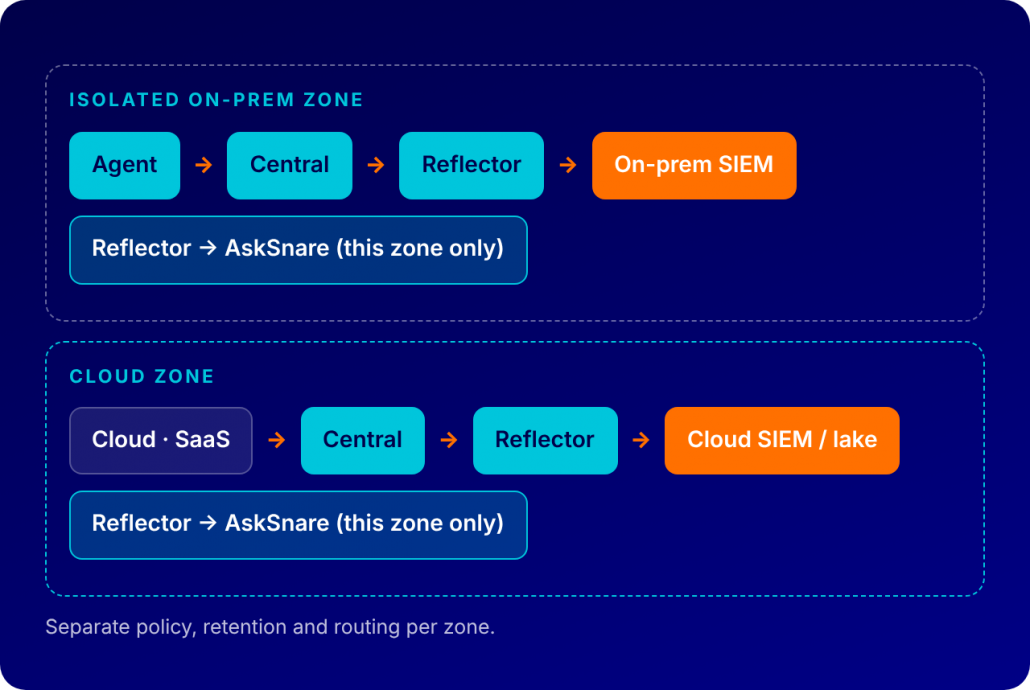
Snare can be deployed four ways: (1) fully on-premises, with Snare Agent, Central and Reflector inside your environment; (2) on-premises plus AskSnare for AI-assisted investigation; (3) unified collection, bringing on-premises and cloud sources into one Snare Central; and (4) hybrid/separated, extending to cloud sources while keeping an isolated on-premises zone with its own policy and routing.
Which deployment pathway should I choose?
Start from your strictest data-residency requirement. If logs must stay on-premises, choose Pathway 01, or Pathway 02 if you also want AI-assisted investigation. If you want one collection approach across on-premises and cloud, choose Pathway 03. If you are adopting cloud but need strict separation between zones, choose Pathway 04.
Does Snare replace my SIEM?
No. Snare is a complementary security data layer that sits alongside your existing SIEM and XDR tools. It collects, retains and routes log data so your SIEM receives the events it needs for detection, while the complete record stays available in Snare Central for search, compliance and replay.
Can I move between pathways later?
Yes. Because Snare separates collection from analysis, changing pathways means adding a component (such as AskSnare) or a new zone or destination, not re-deploying agents or re-collecting data.
Is AskSnare available in an on-premises deployment?
Yes. Pathway 02 is designed for exactly that: AskSnare runs over the data you already retain on-premises. Its federated design means queries execute in place and no data is replicated to answer them.
How long can Snare retain log data?
Retention is fully customisable, from 90 days to 7+ years. Compressed, native-format storage delivers 90–98% storage savings at rest, making multi-year retention practical for compliance and forensic investigation.
How does Snare reduce SIEM costs?
Snare filters data before it reaches the SIEM, so you pay to ingest only the events you need analysed in real time. Everything else is retained affordably in Snare Central and can be replayed into the SIEM on demand. Customers have reported ingestion reductions of up to 60%, depending on source mix, filtering policy and SIEM licensing.