One security data platform. ONE TWO THREE FOUR ways to deploy it

Snare collects, retains, routes and investigates security log data alongside the SIEM and XDR tools you already run. Choose the deployment pathway that fits your data sovereignty, cloud and investigation requirements, then adapt it as those requirements change.

Secure logging. Intelligent investigation.

4000+

Customers

2.5M+

Enterprise agents deployed

90-98%

Storage savings at rest

25+yrs

In production

The Snare platform

Every pathway runs on the same four-stage pipeline

Snare is the security data layer between your log sources and your analytics tools. It captures forensic-grade data everywhere you need it, keeps it affordably, sends each destination exactly what it needs, and makes the whole estate answerable in plain English. Your SIEM keeps doing detection; Snare makes the data feeding it complete, controlled and cost-efficient.

Collect

Snare Agent

Lightweight, tamper-resistant agents for Windows, Linux, macOS and network devices. Logs are cached locally, encrypted and filtered at source before forwarding, with up to 256 simultaneous destinations per agent.

Retain & replay

Snare Central

Aggregates on-premises and cloud sources, applies compliance policy and stores compressed history with 90–98% storage savings at rest. Log Replay sends only the historical window you need back to the SIEM.

Route

Snare Reflector

Mirrors or forwards data in real time to multiple SIEMs, XDRs, data lakes, cloud storage and message brokers, with per-destination filtering and schema remapping.

Investigate

AskSnare

A cybersecurity AI assistant, powered by ProDataIQ, that answers plain-English questions over your Snare data. Federated, explainable and human-in-the-loop.

Deployment pathways

Choose the pathway that fits your environment

This is a decision guide, not a ranking. Every pathway delivers the full value of the Snare platform. The difference is where your data lives, how your cloud sources are handled, and whether AI-assisted investigation is part of day one.

Pathway 01

Fully On-Premises

Agent, Central and Reflector run entirely inside your environment. Collection retention and routing never leave your network


Best for: strict data sovereignty network isolation, or policy that keeps logs on-premises

Pathway 02

On-Premises + AskSnare

The same on-premises architecture with AI Assisted investigation over the data you already retain


Best for: SOC teams that want faster answers without changing where the data lives.

Pathway 03

Unified collection

On-Premises and cloud sources flow into one Snare Central with the same routing and SIEM Cost controls across the estate


Best for: Mixed estates that want one consistent collection approach

Pathway 04

Hybrid/ Separated

Extend into cloud sources while keeping an isolated on-premises zone. Each zone has its own policy and routing.


Best for: Regulated or sensitive environments adopting cloud with strict separation

Your requirement01 · Fully on-prem02 · On-prem + AskSnare03 · Unified collection04 · Hybrid / separated
Keep all logs on-premisesStrong fitStrong fitOptionalStrong fit (isolated zone)
AI-assisted investigationNot includedCore reasonAvailableAvailable
Collect cloud and on-prem sourcesLimitedLimitedCore reasonSupported, in separate zones
Isolated data zonesSupportedSupportedNot a primary focusCore reason
One collection approach across the estateOn-prem onlyOn-prem onlyYesPer zone

Inside each pathway

How data flows in each deployment

PATHWAY 01

Fully on-premises

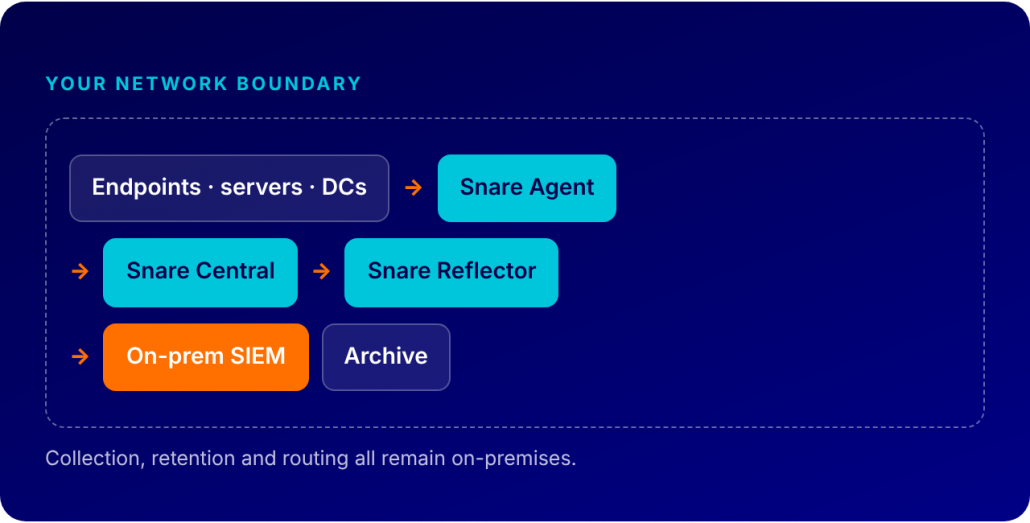
The complete Snare pipeline runs inside your own infrastructure. Nothing about collection, storage or routing depends on an external service.

  1. Snare Agents on endpoints, servers and domain controllers collect events, cache them locally and forward them encrypted.
  2. Snare Central receives everything, compresses it and retains it for anywhere from 90 days to 7+ years, according to your policy.
  3. Snare Reflector filters and forwards the events your detections need to your on-premises SIEM, and mirrors full streams to an archive or a second tool if required.

Best for: defence, government, critical infrastructure and any organisation where logs must remain inside a controlled network boundary.

PATHWAY 02

On-premises + AskSnare

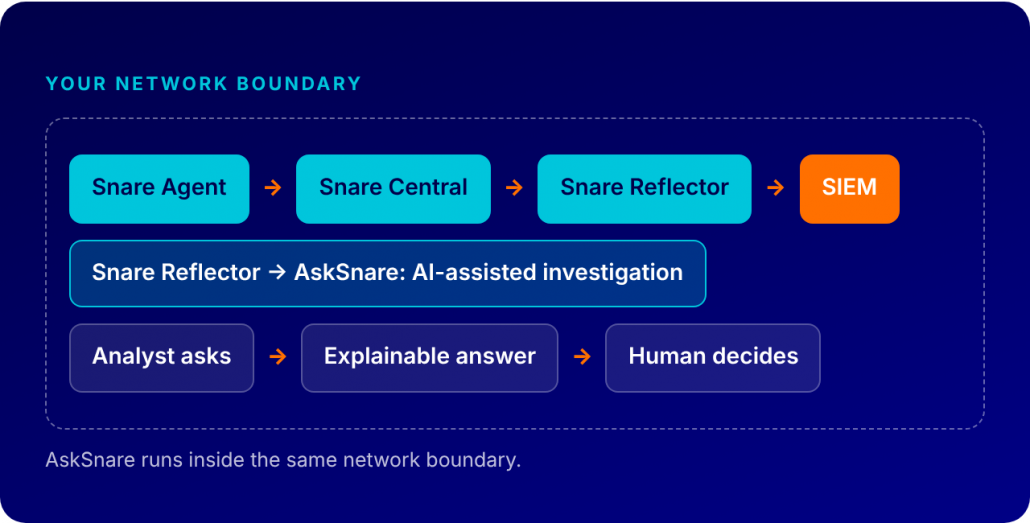
Keep the architecture from Pathway 01 and add AskSnare, so analysts can investigate retained data in plain English instead of building searches and dashboards by hand.

  1. Collection, retention and routing work exactly as in Pathway 01.
  2. Snare Reflector routes log data to AskSnare alongside your SIEM and other destinations, so analysts can investigate in plain English.
  3. Every answer includes auditable reasoning, and anomaly findings come with recommended next steps. An analyst makes the final decision.

Best for: SOC teams that want to shorten investigations without changing where their data lives.

PATHWAY 03

Unified collection

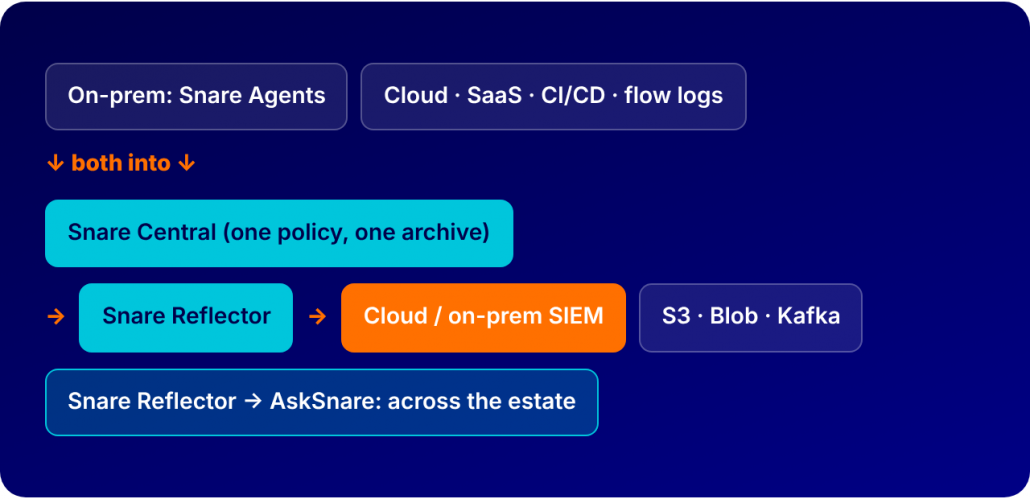
Bring on-premises and cloud sources into one Snare Central, so the whole estate follows a single collection, retention and routing policy.

  1. Snare Agents cover on-premises systems; SaaS, cloud workload, network and CI/CD sources (including OCI VCN flow logs) send directly to Snare Central.
  2. The same filtering and SIEM cost controls apply to every source, with schema remapping templates for Splunk CIM and Microsoft Sentinel ASIM.
  3. Reflector routes to cloud or on-premises SIEMs, AWS S3, Azure Blob Storage, GCP, Kafka or EventBridge. AskSnare is available across the unified data set.

Best for: mixed estates and organisations mid-migration to cloud that want one consistent approach rather than a separate pipeline per environment.

PATHWAY 04

Hybrid / separated

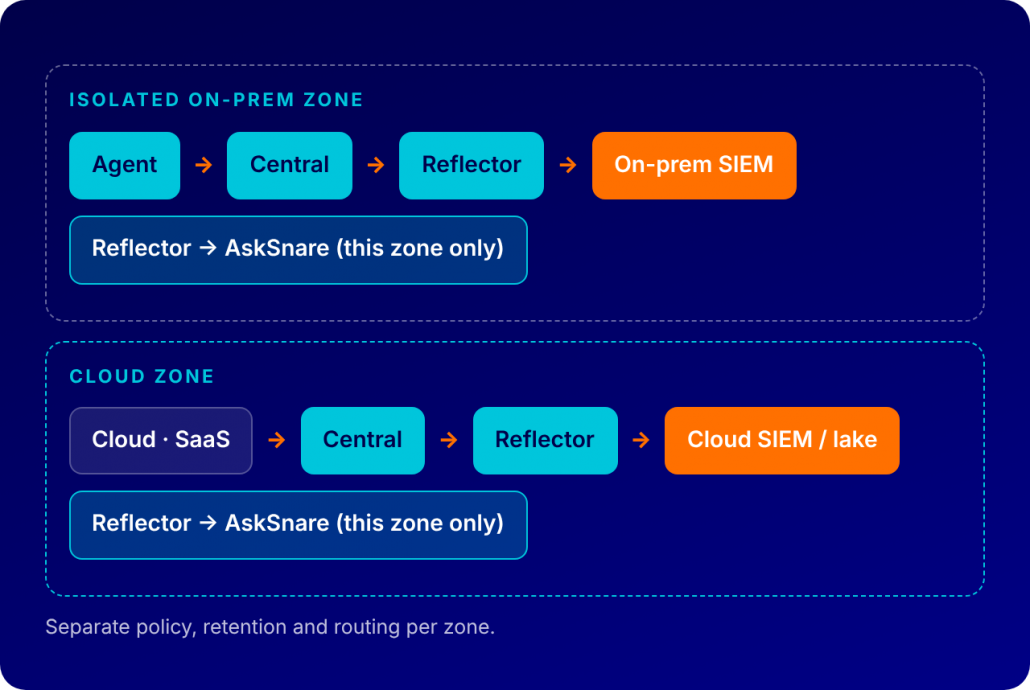
Adopt cloud sources while keeping a sealed on-premises zone. Each zone runs its own Snare policy and routing, so sensitive data never mixes with cloud data.

  1. The isolated on-premises zone collects, retains and routes exactly as in Pathway 01.
  2. A separate cloud zone collects cloud and SaaS sources under its own retention and routing policy.
  3. Each zone forwards to its own destinations. AskSnare can be enabled per zone, so investigation respects the same separation.

Best for: regulated and sensitive environments, such as financial services, healthcare and government, that are adopting cloud but must keep strict separation between data classifications.

Built to change with you

A pathway, your choice!

Your first deployment doesn’t lock you in. Because collection is decoupled from analysis, moving between pathways means adding a component or changing a destination, not re-instrumenting your estate.

01 → 02

Add AI-assisted investigation

Enable AskSnare over the data you already retain. No new collection and no data movement.

01 / 02 → 03

Bring cloud sources in

Point cloud and SaaS sources at Snare Central and apply the policy you already run on-premises.

01 / 02 → 04

Extend with separation

Stand up a cloud zone alongside your sealed on-premises zone, each with its own policy and routing.

In every pathway

What you get, whichever way you deploy

Forensic-grade collection

Encrypted, tamper-evident logs with chain-of-custody preserved from source to storage, built to stand up in audit, litigation and breach response.

90–98% storage savings at rest

Compressed, native-format retention makes long-term history affordable, so you don’t have to trade coverage for cost.

Retention on your terms

From 90 days to 7+ years, fully customisable to the regulatory and investigative windows that apply to you.

Log Replay

Push only the historical window an investigation or auditor needs back into your SIEM, instead of keeping years of data hot.

Vendor-agnostic routing

Native delivery to Splunk, Microsoft Sentinel, IBM QRadar, Securonix, Elastic, OpenSearch, Devo, Chronicle and Secureworks Taegis, in parallel or during a migration.

Search & compliance reporting

Basic and advanced search, saved and scheduled queries, and out-of-the-box reports aligned to ISO 27001, PCI DSS, HIPAA, NIST CSF, SOX, NERC, GDPR and Essential Eight.

Working alongside your SIEM

How Snare fits into your existing SIEM architecture

Snare complements your SIEM rather than replacing it. Your detection content, dashboards and workflows stay where they are; Snare controls what reaches them and keeps everything else available.

Receive everything

Existing universal or heavy forwarders send 100% of their data to Snare, so nothing is dropped at the edge.

Store & compress

Snare Central keeps the complete record in native format, searchable and compliance-ready.

Filter to the SIEM

Only the events your detections and dashboards need are forwarded to SIEM indexers.

Reflect elsewhere

Full or partial streams go to S3, data lakes or a second SIEM, with no duplicate collection.

Replay on demand

Historical windows return to the SIEM when an investigation or audit calls for them.

What this changes: customers have reported SIEM ingestion reductions of up to 60% by filtering before the SIEM. Results depend on source mix, filtering policy and SIEM licensing model. It also reduces the number of heavy forwarders you need to run, and changing SIEMs becomes a change of destination rather than a re-collection project. Model your own savings with the ROI calculator.

NIST SP 800-92

Supports log management practices for generation, transmission, storage and disposal across the estate.

NIST SP 800-92

Supports log management practices for generation, transmission, storage and disposal across the estate.

ISO/IEC 27001:2022 A.8.15

Provides the logging evidence and log protection the Annex A logging control calls for.

PCI DSS v4.0 Req. 10

Retains audit history for at least 12 months, with Log Replay for the most recent three months that must be immediately available.

ASKSNARE

AI-assisted investigation that clears governance review

AskSnare is a cybersecurity AI assistant for your analysts, not an autonomous AI SOC agent. It answers questions over your Snare data and recommends next steps. Your team stays accountable for every decision.

Federated

Queries execute where the data already lives. Nothing is replicated or moved to answer a question, which simplifies sovereignty review.

Explainable

Every answer includes auditable reasoning, so analysts can verify how a conclusion was reached.

Human-in-the-loop

Real-time anomaly detection surfaces recommended actions. It does not perform autonomous remediation.

Built on forensic-grade data

Answers draw on chain-of-custody-protected Snare data, so AI outputs inherit the same integrity.

Ready to see Snare in action? Book a demo now or contact us to learn more.

FAQ

How Snare works: common questions

What are the four Snare deployment pathways?

Snare can be deployed four ways: (1) fully on-premises, with Snare Agent, Central and Reflector inside your environment; (2) on-premises plus AskSnare for AI-assisted investigation; (3) unified collection, bringing on-premises and cloud sources into one Snare Central; and (4) hybrid/separated, extending to cloud sources while keeping an isolated on-premises zone with its own policy and routing.

Which deployment pathway should I choose?

Start from your strictest data-residency requirement. If logs must stay on-premises, choose Pathway 01, or Pathway 02 if you also want AI-assisted investigation. If you want one collection approach across on-premises and cloud, choose Pathway 03. If you are adopting cloud but need strict separation between zones, choose Pathway 04.

Does Snare replace my SIEM?

No. Snare is a complementary security data layer that sits alongside your existing SIEM and XDR tools. It collects, retains and routes log data so your SIEM receives the events it needs for detection, while the complete record stays available in Snare Central for search, compliance and replay.

Can I move between pathways later?

Yes. Because Snare separates collection from analysis, changing pathways means adding a component (such as AskSnare) or a new zone or destination, not re-deploying agents or re-collecting data.

Is AskSnare available in an on-premises deployment?

Yes. Pathway 02 is designed for exactly that: AskSnare runs over the data you already retain on-premises. Its federated design means queries execute in place and no data is replicated to answer them.

How long can Snare retain log data?

Retention is fully customisable, from 90 days to 7+ years. Compressed, native-format storage delivers 90–98% storage savings at rest, making multi-year retention practical for compliance and forensic investigation.

How does Snare reduce SIEM costs?

Snare filters data before it reaches the SIEM, so you pay to ingest only the events you need analysed in real time. Everything else is retained affordably in Snare Central and can be replayed into the SIEM on demand. Customers have reported ingestion reductions of up to 60%, depending on source mix, filtering policy and SIEM licensing.
Snare Solutions
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.